

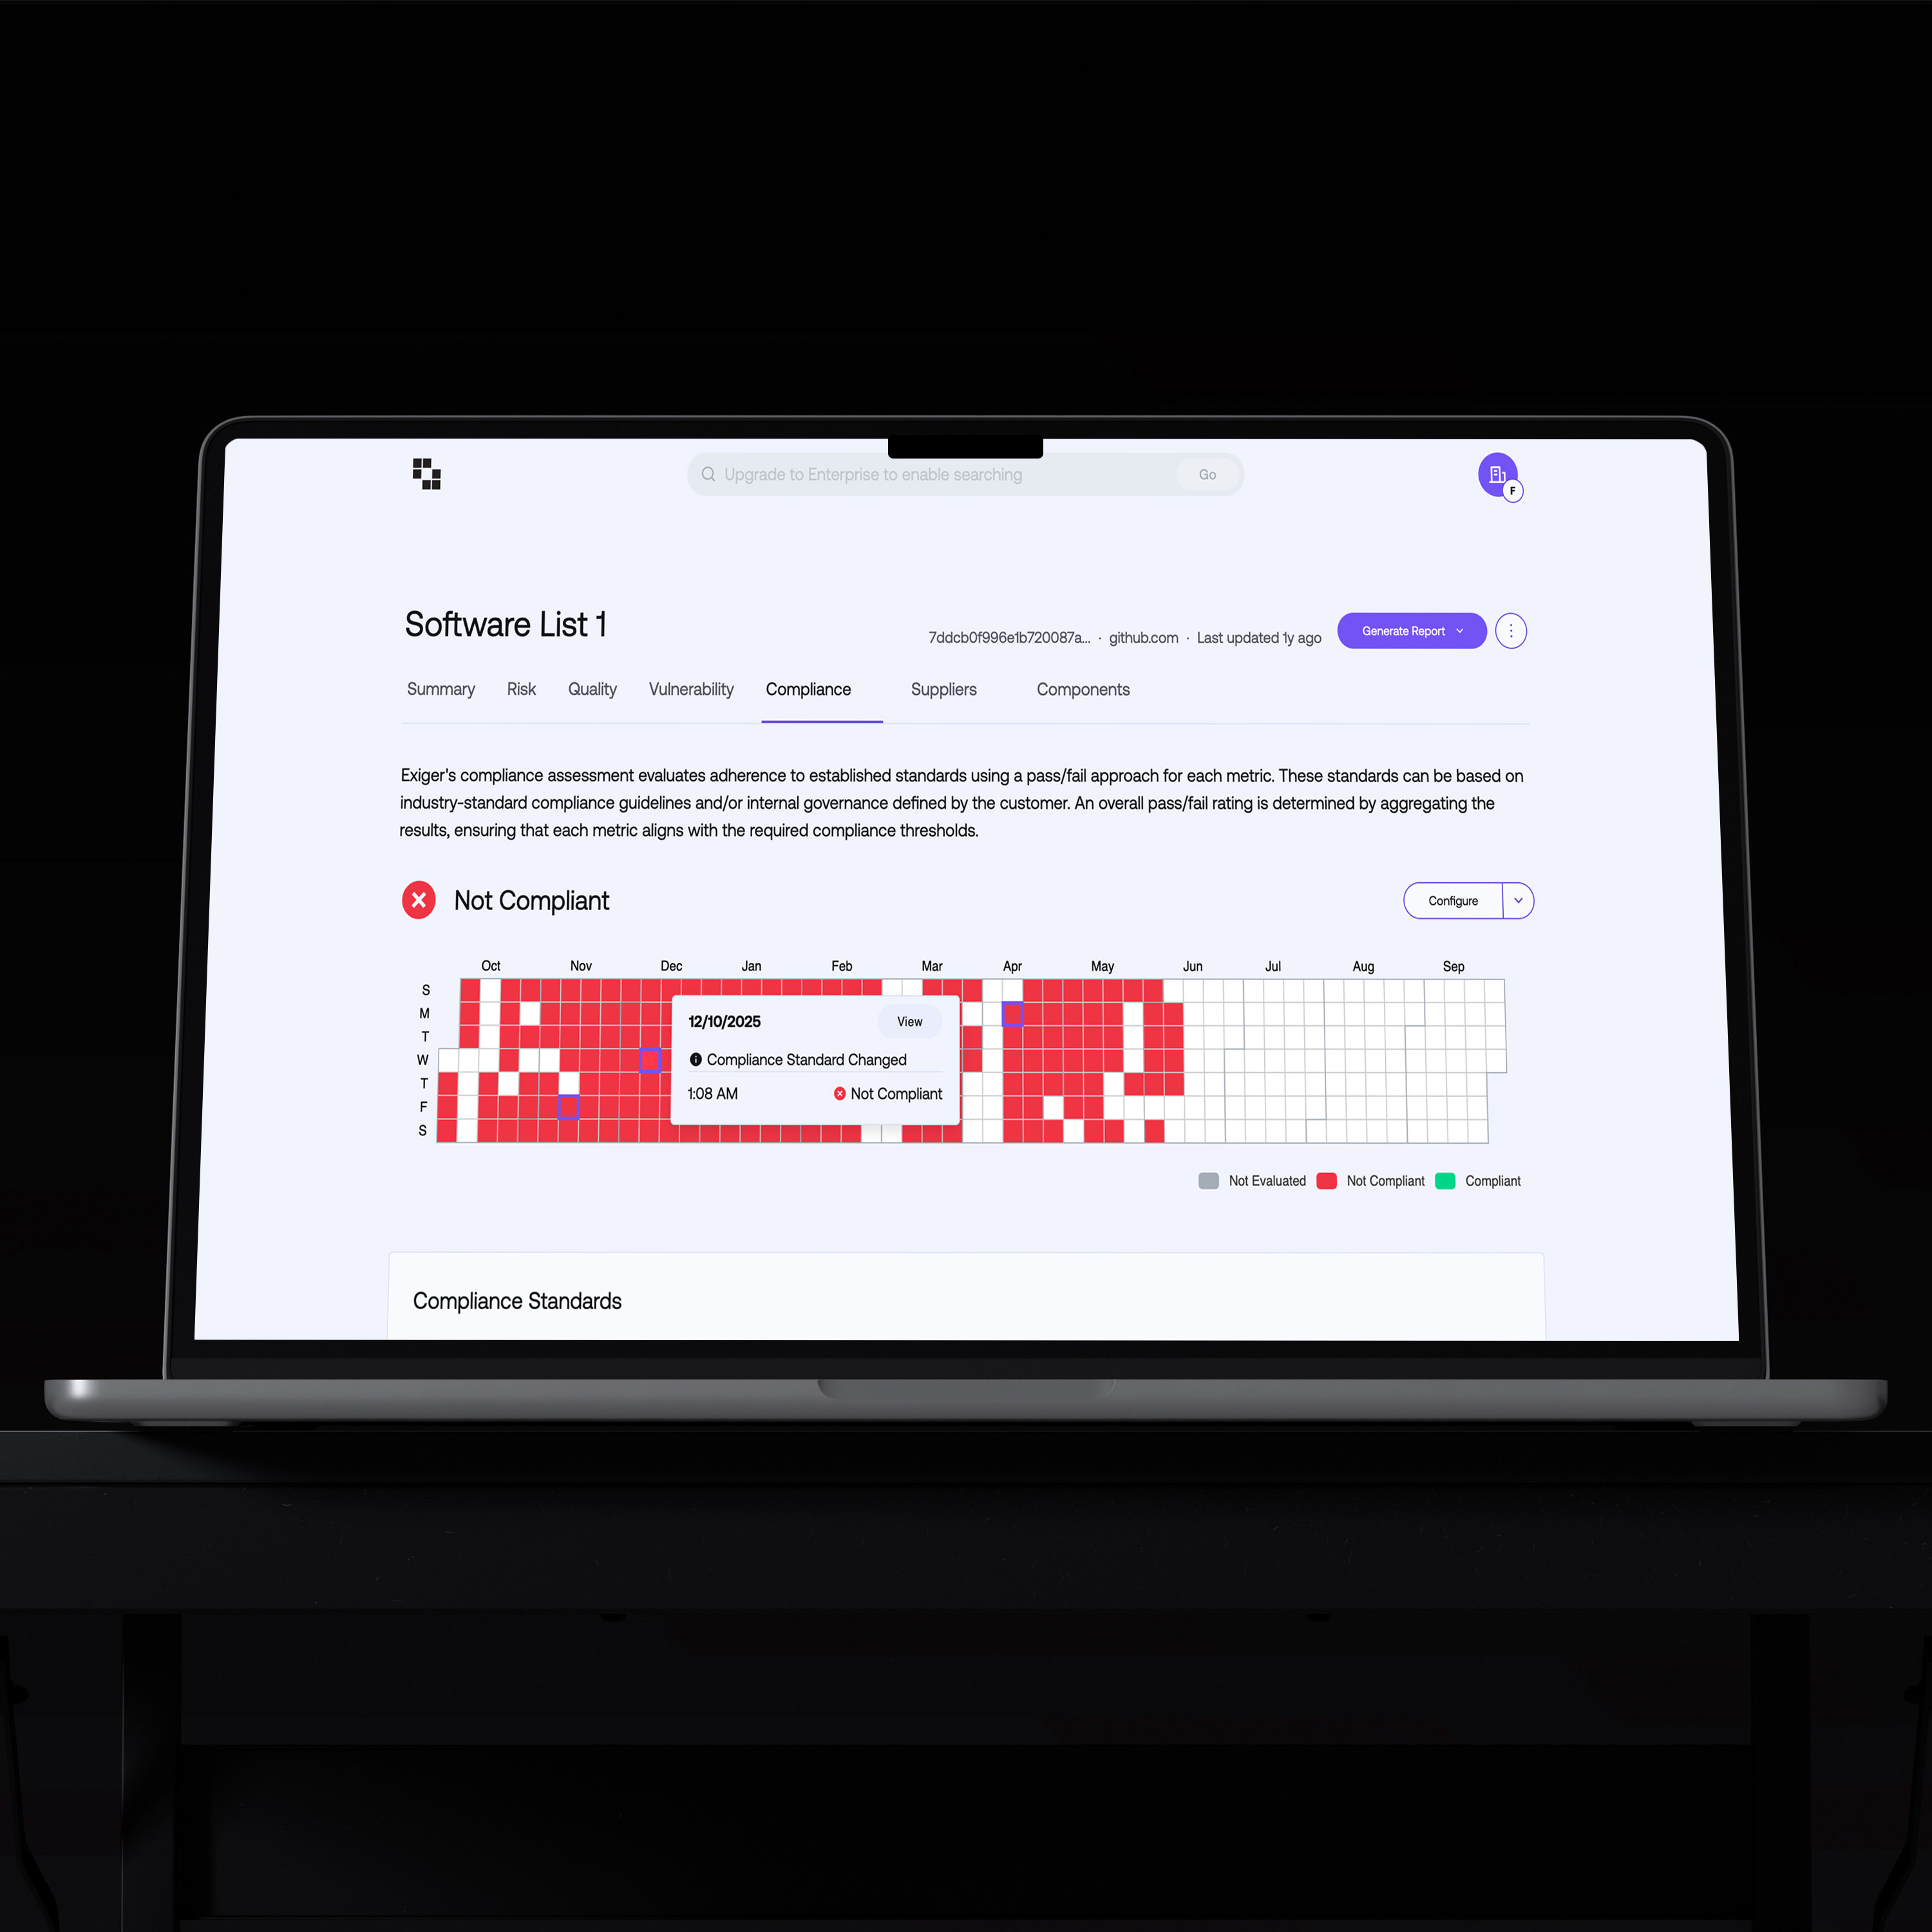
More Than Just an SBOM Tool
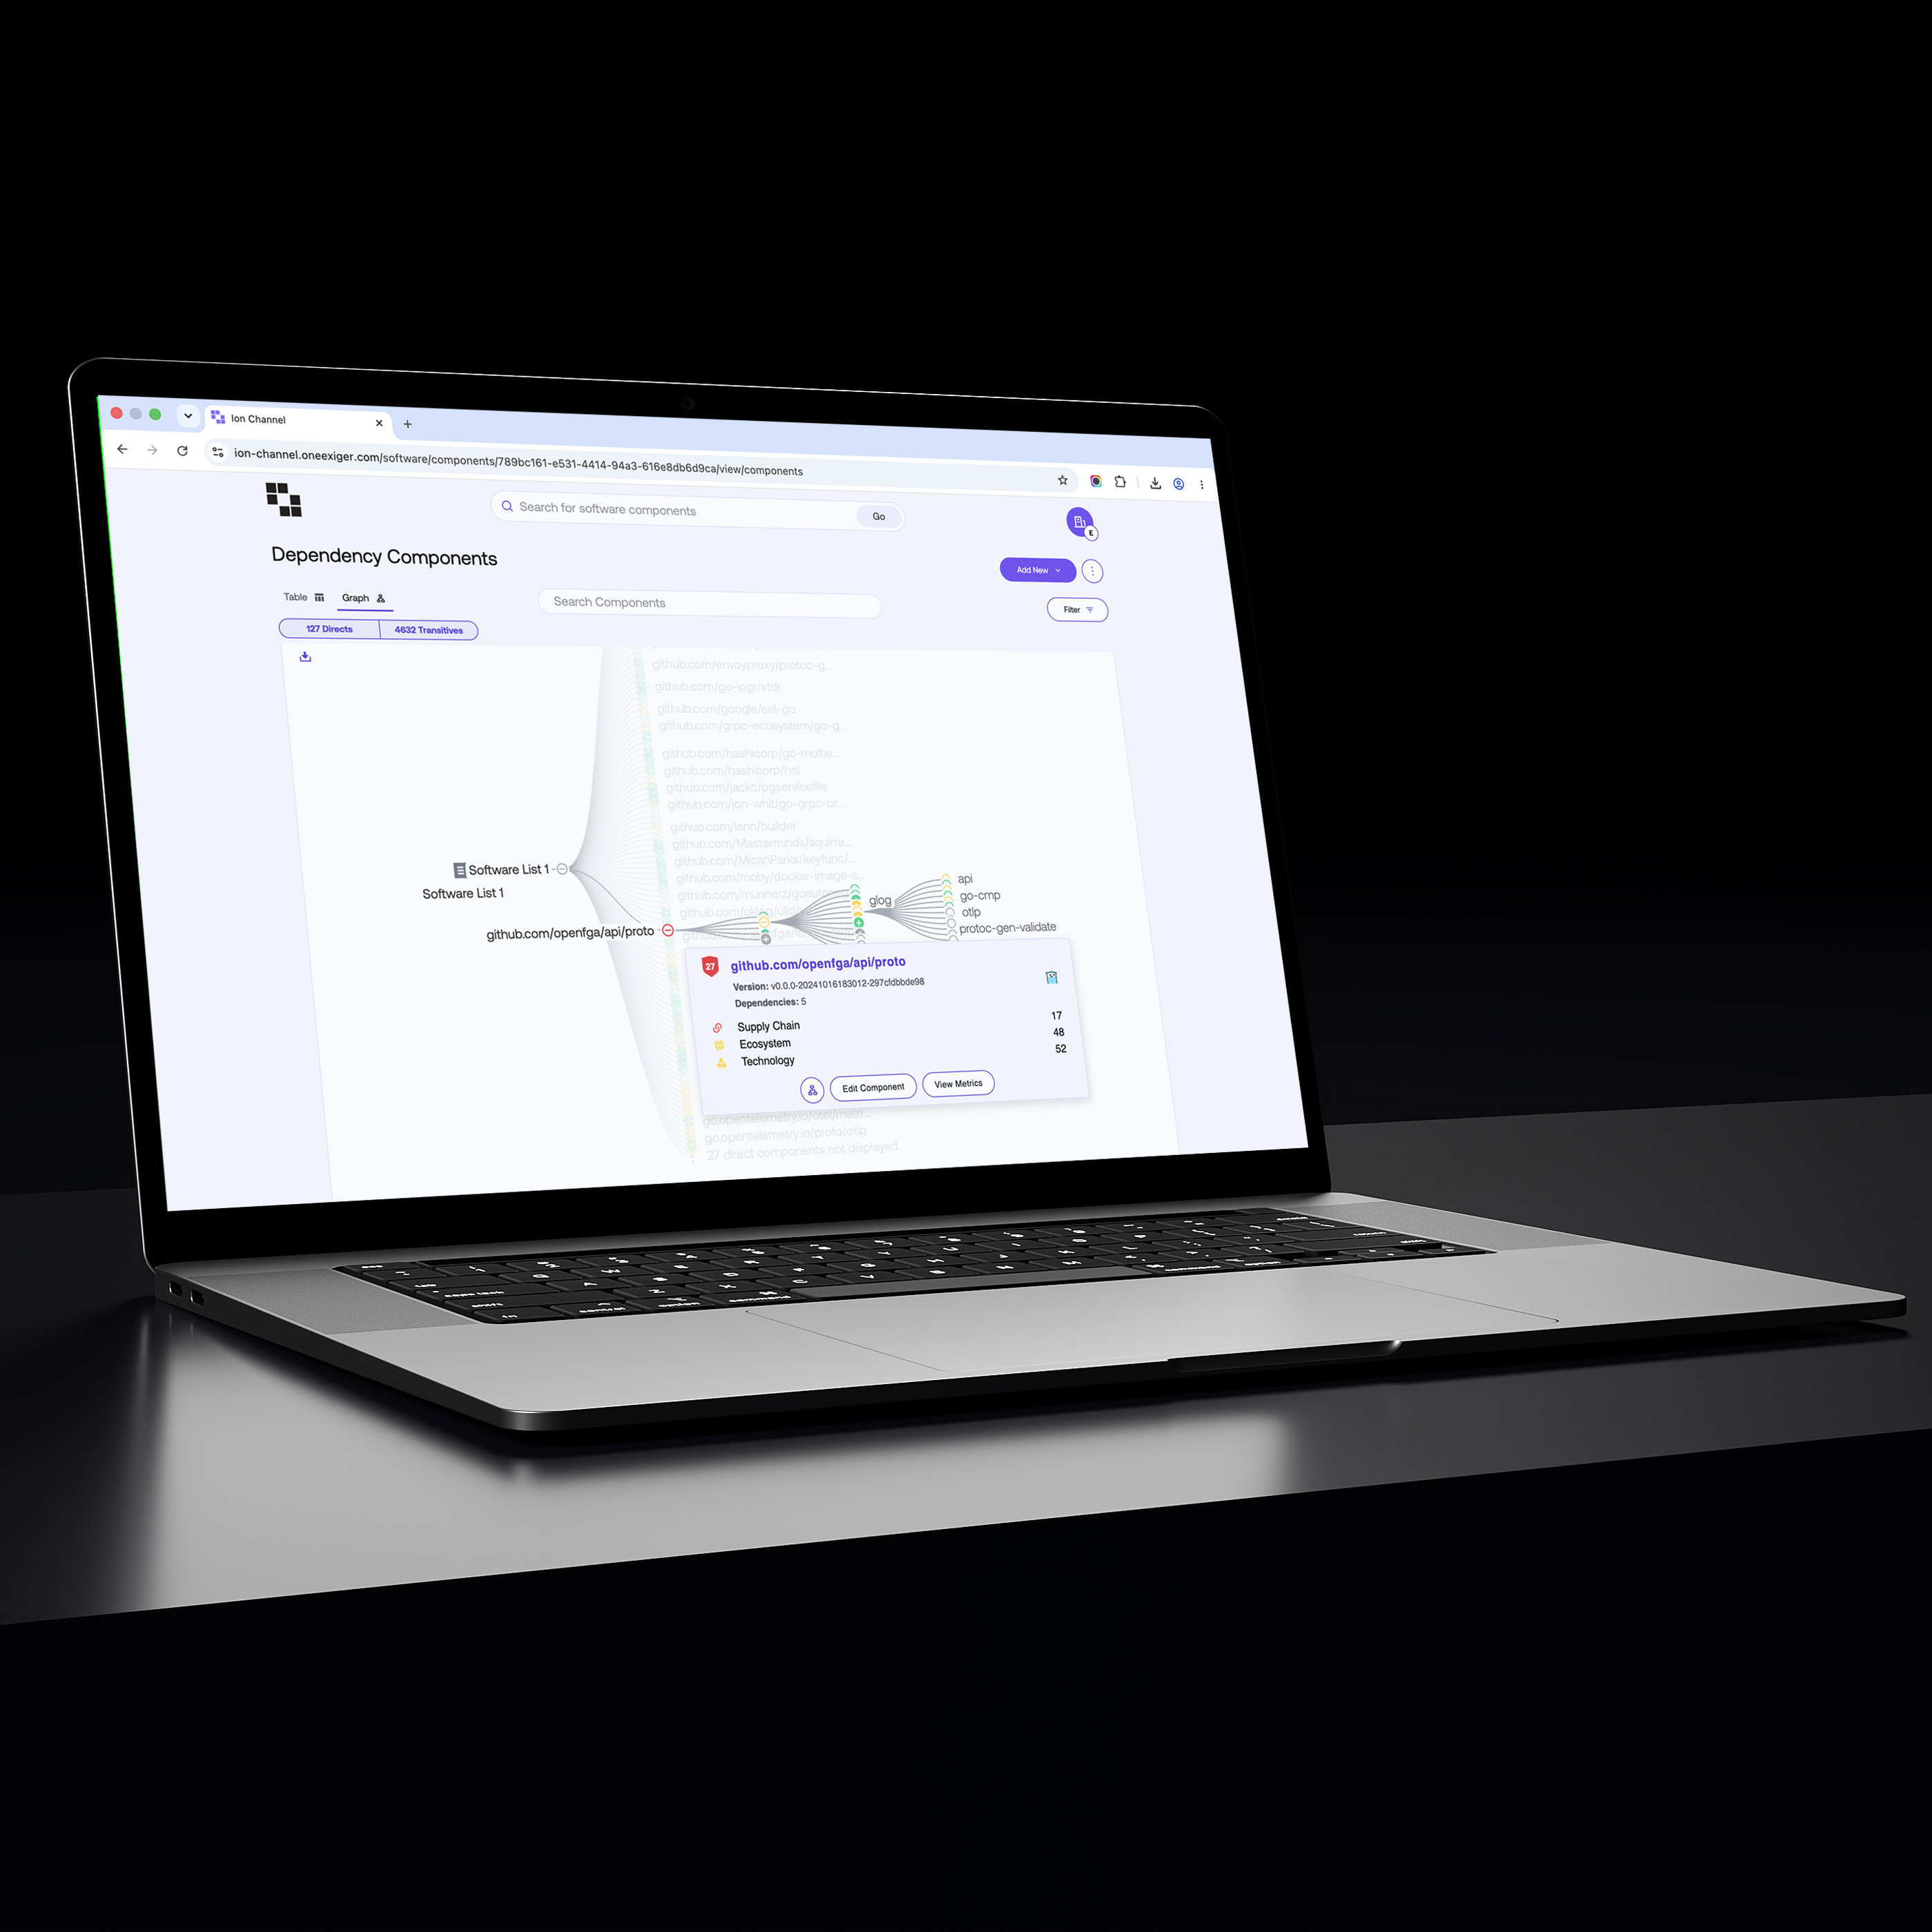
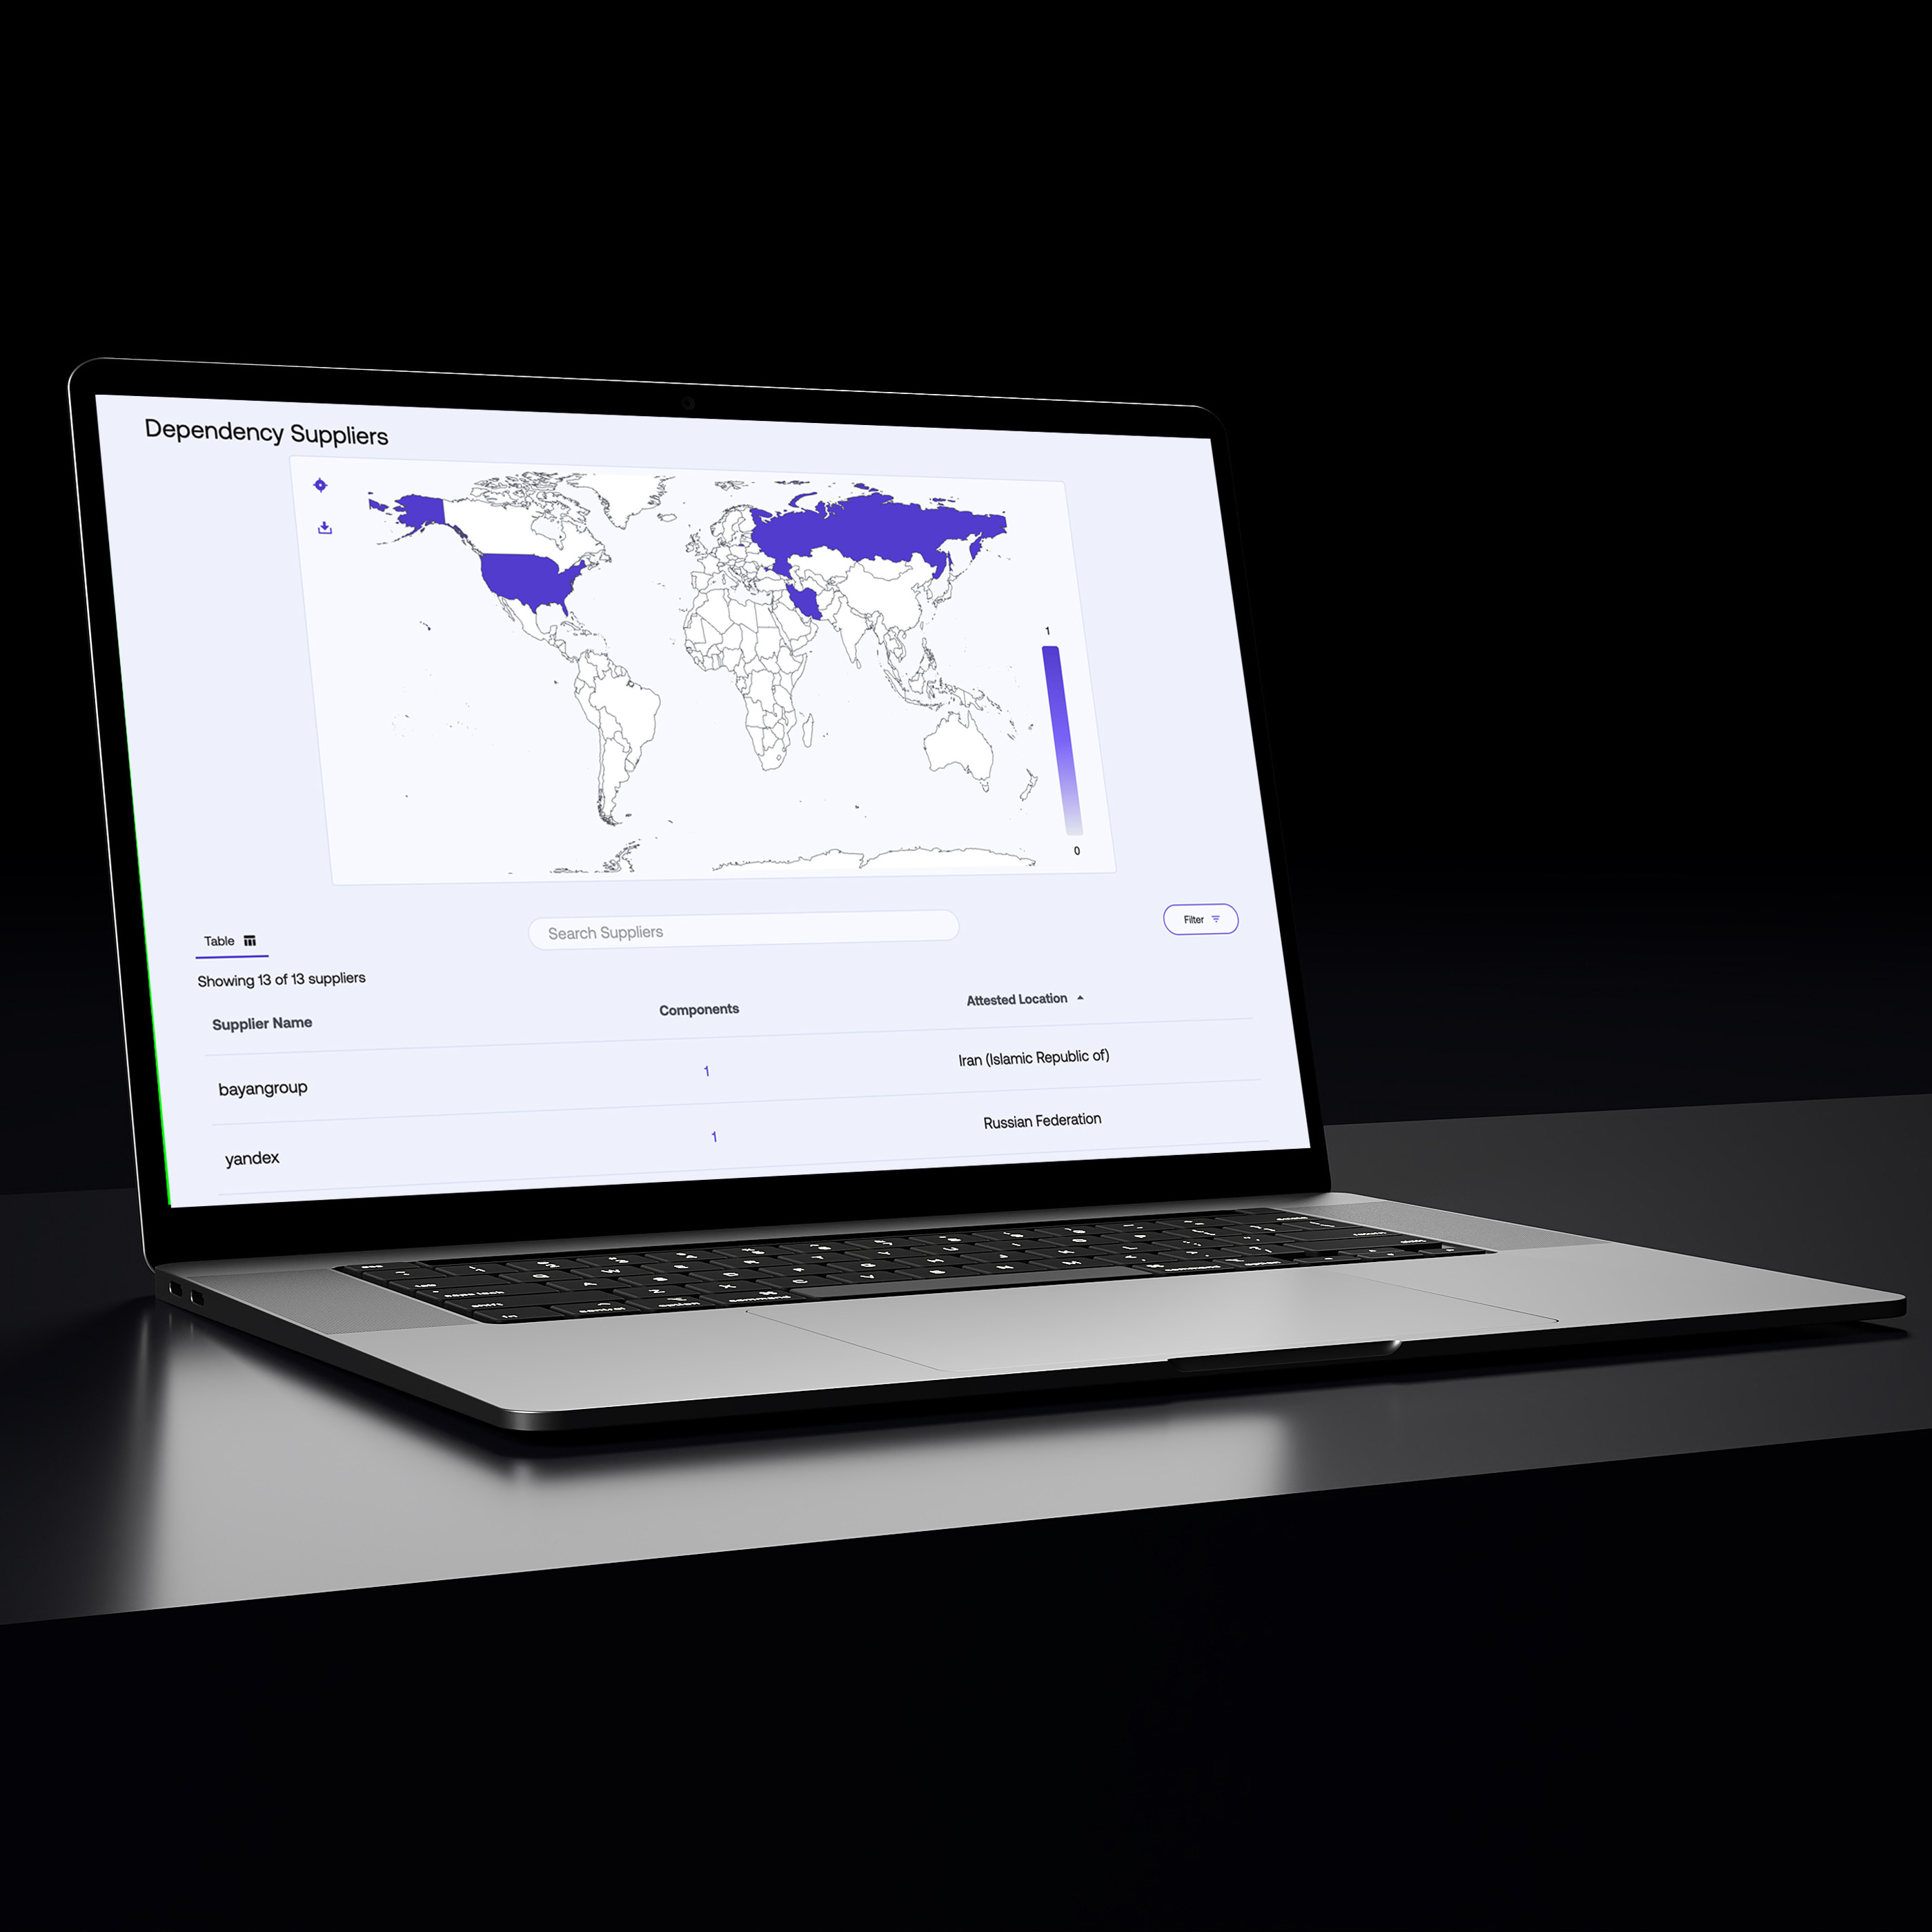
Other cybersecurity tools excel in one lane. We Exiger connects software, binaries, suppliers, and enterprise risk into a single view.
SBOM-Only Tools
Tools in this category focus on generating or validating software bills of materials and dependency graphs. They excel at visibility into open source and known components.
Blind Spots: They typically do not assess supplier or entity risk, binary and malware analysis, or threat intelligence in a unified way. Compliance and executive reporting often require separate processes.
Exiger Advantage: Connects SBOM visibility to supplier intelligence, binary analysis, and compliance in one platform so you can move from detection to decision.
Compliance & Vulnerability Tools
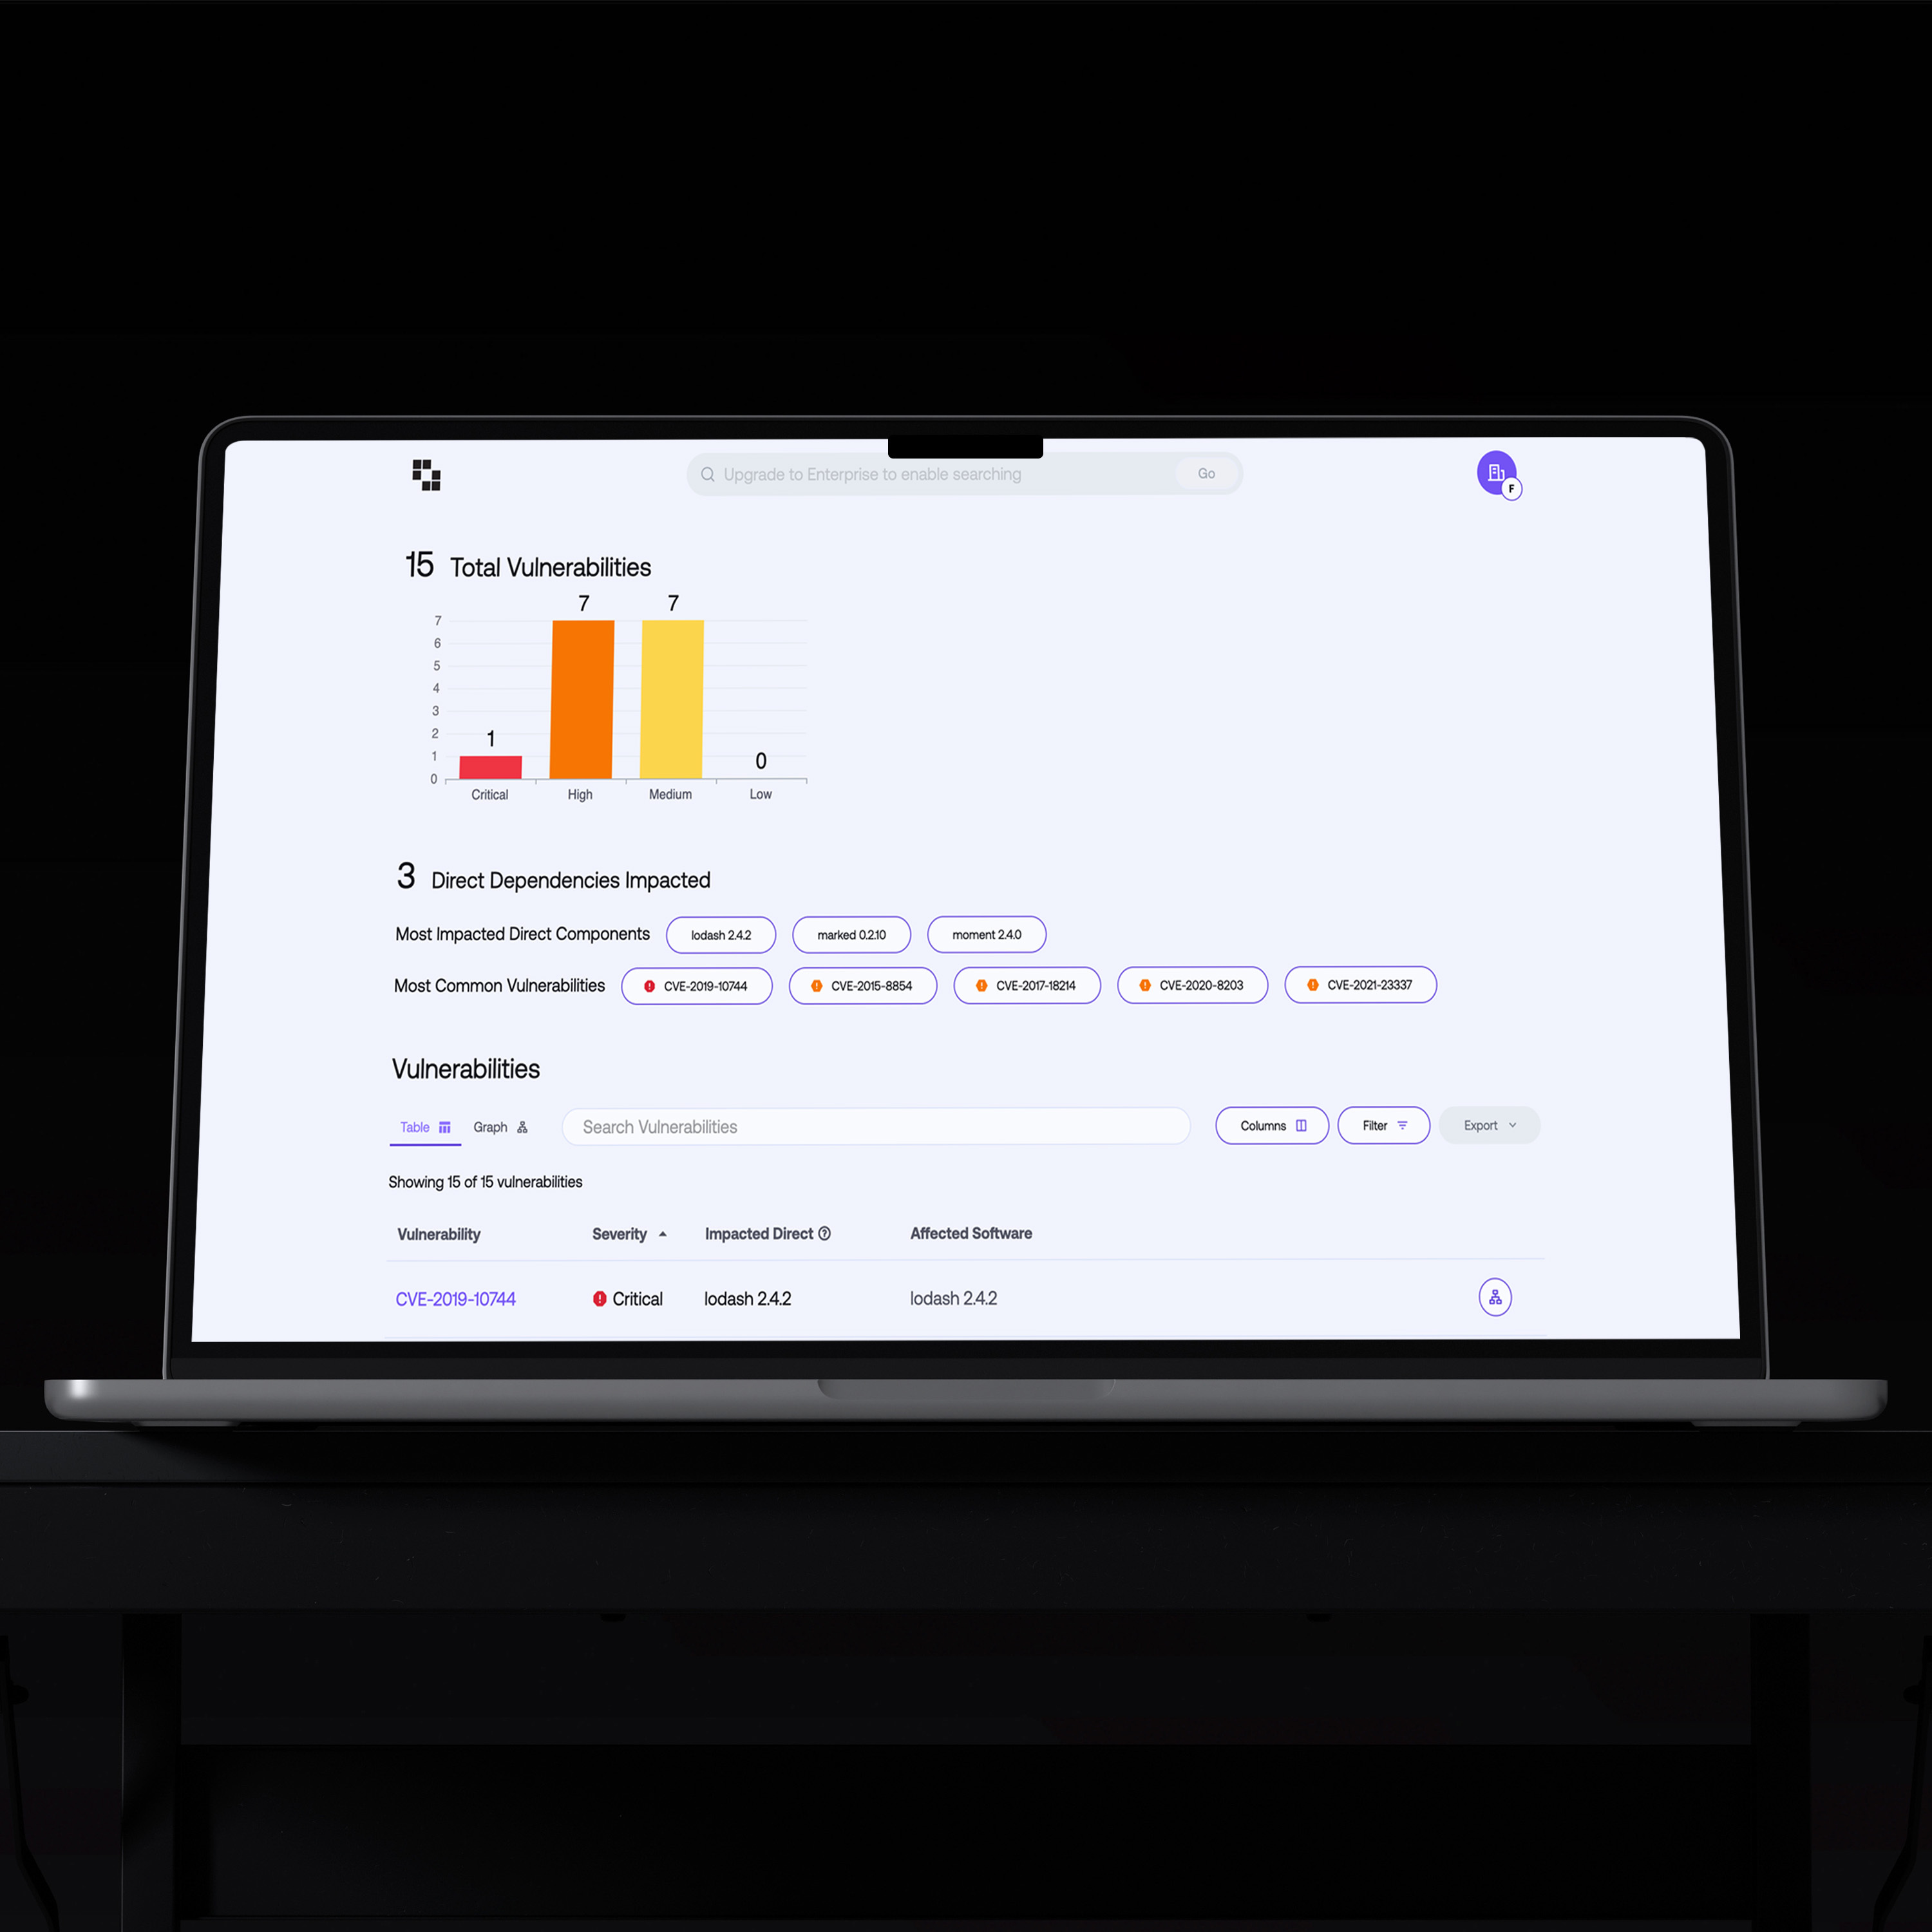
These tools emphasize vulnerability scanning, patch management, and compliance dashboards. They help teams track CVEs and meet baseline security controls.
Blind Spots: They often lack deep software supply chain context: who built the component, who owns the supplier, and how it fits into your products. SBOM and supplier risk are usually out of scope.
Exiger Advantage: Integrates vulnerability and compliance outcomes with software and supplier context, giving you one place to operationalize compliance and reduce risk.
Binary-First Tools
These tools specialize in analyzing executables, firmware, and packaged artifacts. They excel at malware detection and binary-level visibility.
Blind Spots: They typically do not provide SBOM generation, supplier risk (e.g., FOCI, sanctions), or product-level risk visibility. Software and supplier context live elsewhere.
Exiger Advantage: Combines binary analysis with SBOM, supplier intelligence, and product-level views so you get one integrated picture of software and supply chain risk.
Network Detection Tools
Network-focused tools detect anomalies, intrusions, and lateral movement across the corporate network. They are critical for runtime and environment security.
Blind Spots: They do not address the software supply chain: what's in your code, who built it, or how it maps to products and compliance. That visibility requires a different lens.
Exiger Advantage: Focuses on software supply chain risk — what you build and buy — and complements network security with actionable intelligence on components, suppliers, and products.